Owners and general managers
You need a plain account of what happened, what it means for the business, and what to fix first.
An alert you don’t recognise. A login from somewhere new. A customer asking about an email you never sent. When something doesn’t look right, you need clear answers: what happened, what was affected, and what to do next. ARA Industries helps you find out, keep the evidence intact and recover with a plan.
Email securenow@ara.ph with “Incident” in the subject, or use the contact form and choose how urgent it is. Tell us your name, organisation, a number we can reach you on, and a one-line description of what you noticed.
Please don’t send passwords, evidence files or personal data by email or through the form. We’ll arrange a secure way to collect what’s needed.
Teams and organizations of 20 to 500 people, anywhere in the world, that need to understand a security incident and act on facts.
You need a plain account of what happened, what it means for the business, and what to fix first.
You need experienced hands, a documented method, and findings your team can act on.
You need clear technical facts to assess a possible personal data breach and decide on notifications.
Six steps, from the first conversation to a stronger environment. Each step is documented so the work is consistent and repeatable.
We learn what happened, how it affects the business, which systems are involved, what evidence exists and what concerns you most. Together we agree the scope, priorities and response approach.
We identify the relevant digital evidence, then preserve and acquire it using forensically sound procedures: documented handling, integrity verification and chain-of-custody records where applicable.
We examine the relevant systems, endpoints, logs, network artefacts and files to find suspicious activity, build a timeline and identify indicators of compromise, following documented, standardised procedures.
We reconstruct the incident from the evidence: how the attacker likely got in, how far they reached, whether data may have been exposed, and any persistence or lateral movement.
You receive a structured report covering the findings, supporting evidence, incident timeline, assessed scope and impact, technical conclusions and recommended fixes.
We help you and your stakeholders plan containment, eradication, recovery and prevention, and follow up with technical guidance to strengthen controls and lower the chance of a repeat.
Scoping and investigating suspected or confirmed security incidents.
Preserving and acquiring evidence with documented, verifiable handling.
Examining devices, servers, cloud and application logs.
Analysing suspicious files to understand what they do.
Searching for indicators of compromise across your environment.
Rebuilding the timeline of what happened and why.
Assessing whether data may have left your systems, and which data.
Clear reports with prioritised remediation steps.
Every engagement is tailored to your environment, the severity of the incident, your business needs and what the investigation must answer.
We work only with proper written authorisation, under confidentiality and with evidence-handling controls. Our investigations follow forensically sound practices, documented procedures and repeatable analysis methods, so the findings are reliable, traceable and clearly explained to your management, regulators or legal counsel.
The Data Privacy Act of 2012 (RA 10173, Sec. 20(f)) requires personal information controllers to promptly notify the National Privacy Commission and affected individuals of qualifying breaches. NPC Circular 16-03 (Secs. 17–18) sets a 72-hour window from knowledge or reasonable belief of a breach. We give your DPO and counsel the technical facts they need to decide; the decision and the notification stay with your organisation.
The best investigations start with good logs, tested backups and a one-page incident response plan. We can help you prepare.
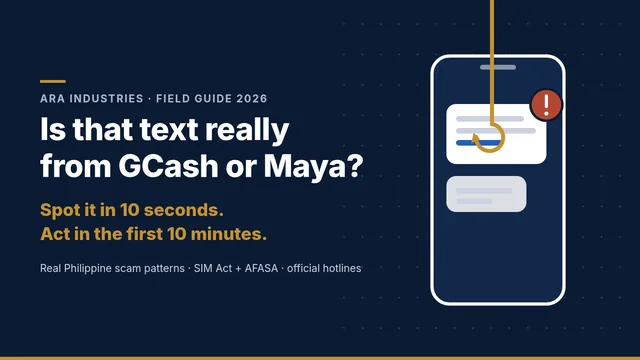
GCash and Maya say they never text links or ask for your OTP. How to spot a fake in 10 seconds, what to do in the first 10 minutes if you slipped,…
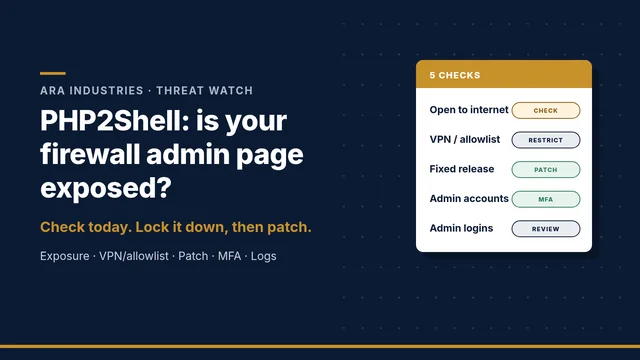
Palo Alto Networks reports active exploitation of the PHP2Shell flaws (CVE-2026-109618, CVE-2026-109619) against PAN-OS management interfaces exposed…
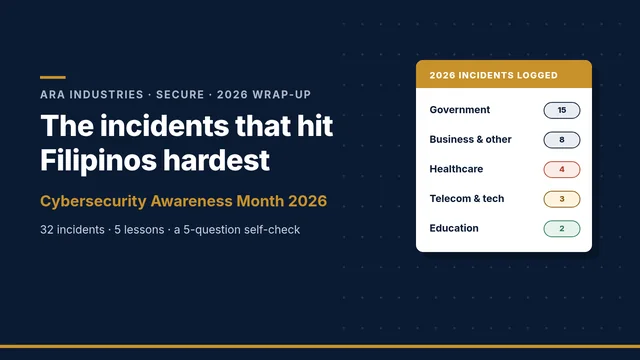
Our Philippine Cyber Incident Map logged 32 incidents in 2026, nine of them confirmed. The five that hit ordinary Filipinos hardest, one lesson from…
DFIR is the work of investigating a security incident to establish what happened, how it happened and how far it reached, while preserving the digital evidence, and then using those findings to contain the incident, recover and prevent a repeat.
Write down what you noticed and when, avoid wiping or reinstalling affected devices, keep a small group informed, tell your Data Protection Officer, and contact us at securenow@ara.ph. Our team will advise on the next steps for your situation, including how to isolate affected systems.
If personal data may be involved, the Data Privacy Act may require the personal information controller to notify the National Privacy Commission and the affected individuals. NPC Circular 16-03 sets a 72-hour window from knowledge or reasonable belief of a personal data breach. Your DPO or legal counsel makes that call; we provide the technical facts they need. This is not legal advice.
Managed Detection and Response watches your environment continuously and responds to threats as they appear. DFIR is an in-depth investigation of a specific incident: what happened, how, and what it affected. Many organisations use both.
No. We work with the systems, logs and security tools you already have. ARA Industries is also a registered WithSecure partner if you want to strengthen detection afterwards.
Yes. ARA Industries is Manila-based, working worldwide. Much of an investigation can be done remotely with your authorisation; onsite work is arranged per engagement.
Each engagement is scoped first, because the effort depends on the number of systems, the evidence available and what the investigation must answer. We confirm the scope and a written quote before work begins.
39 plain-language checks across endpoints, backups, email and identity, patching, admin access, incidents and vendors.
For any Philippine SME or mid-sized business. Enter your details and the download opens on the next page.
Book a free 30-minute Usap Tayo call with the ARA Industries team. For an incident in progress, email securenow@ara.ph instead.
Calendar not loading? Open the Usap Tayo booking page.
Tell us what you need. Please don’t include passwords, evidence files or personal data.
Prefer a call? Book a 30-minute Usap Tayo session.
Cookies on ara.ph
We use strictly necessary storage to run this site. With your permission we also use Google Analytics to see which pages help visitors, and Google Ads measurement to see which ads work. Nothing optional runs until you choose. Privacy policy and cookie list.