PHP2Shell: Attackers Target Exposed Palo Alto Networks Firewall Management Pages
Sources: Palo Alto Networks security advisory · The Hacker News
Palo Alto Networks has updated its security advisory to say that active exploitation has been observed targeting the PAN-OS management interface when it is exposed to the internet. The attacks use two PHP vulnerabilities, known as "PHP2Shell": CVE-2026-109618 and CVE-2026-109619.
If your business runs a firewall from any vendor, this is a good moment to check one simple thing: can anyone on the internet reach your firewall's admin page?
What happened
- 21 October 2026: The PHP project released fixes for two critical flaws (PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35). Both can let an attacker run code remotely without logging in. Palo Alto Networks published its advisory the same day.
- 27 October 2026: Palo Alto Networks raised its rating to Critical (CVSS 9.2) with "Highest" urgency.
- 28 October 2026: The advisory was updated to report active exploitation against management interfaces exposed to the internet. The Hacker News reported on the update.
According to the vendor, the issue affects the management web interface of PAN-OS and Panorama, meaning the HTTPS web UI and the XML API. It affects a dataplane interface only if a management profile is attached to it. The vendor says no special configuration is needed to be affected. It also says the risk is highest when management access is allowed from external internet addresses. GlobalProtect portals and gateways are listed as not affected.
Fixed PAN-OS hotfixes have been released for most supported branches, and a few were still scheduled as of 29 October. Check the vendor's advisory for your exact version. The advisory doesn't say who is behind the attacks or how many devices were compromised, so we won't guess.
Why this matters for Philippine businesses
Firewall and VPN admin pages are made for your IT team, not the public. When they can be reached from the internet, every newly found flaw becomes a direct way in, often before a patch is installed. That pattern isn't unique to one vendor. It's a configuration habit worth fixing on every edge device you own.
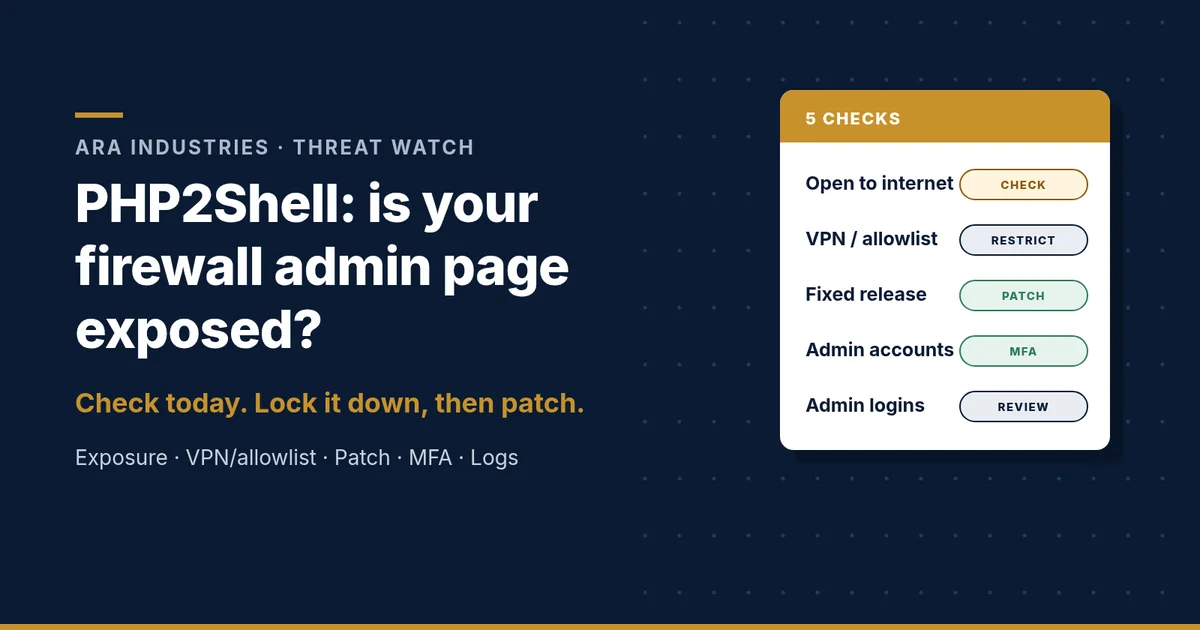
Five checks to run this week
- Find out what's reachable. From outside your office network, test whether your firewall, VPN or router admin page loads. If it does, treat that as the first thing to fix.
- Restrict management access. Allow admin access only from your internal network, a VPN or a dedicated jump host, using an IP allowlist. On PAN-OS, the vendor recommends restricting access to trusted internal IPs.
- Patch. Apply the vendor's fixed release for your version as soon as it's available, and keep a backup of your configuration first.
- Turn on MFA for every administrator account, and remove old or shared admin logins.
- Review logs. Look for unexpected admin logins, configuration changes or unfamiliar files since mid-October. If something looks wrong, get help before you wipe anything, so evidence is preserved.
How ARA Industries can help
ARA Industries is a Manila-based cybersecurity and IT company working worldwide. We can run an external exposure check to show which of your systems, including firewall and VPN admin pages, can be seen from the internet. We then help you lock them down, patch safely and set up ongoing monitoring.
Usap Tayo. Book an exposure check
Sources: Palo Alto Networks security advisory · The Hacker News
Frequently asked questions
What is PHP2Shell?
PHP2Shell is the name used for two critical PHP vulnerabilities, CVE-2026-109618 and CVE-2026-109619, that can allow unauthenticated remote code execution on affected systems. PHP fixed them on 21 October 2026.
Which Palo Alto Networks products are affected?
According to the vendor advisory, the PAN-OS and Panorama management web interface (the HTTPS web UI and XML API) is affected. GlobalProtect is listed as not affected.
Is PHP2Shell being exploited?
Yes. Palo Alto Networks reports active exploitation against management interfaces exposed to the internet.
What should I do first?
Remove internet access to the management interface, restrict it to trusted internal IPs or a jump host, then apply the fixed PAN-OS release for your version.
Does this matter if I use a different firewall brand?
The specific flaw concerns this vendor, but exposed admin pages are a risk on any device. Checking and restricting them is good practice everywhere.